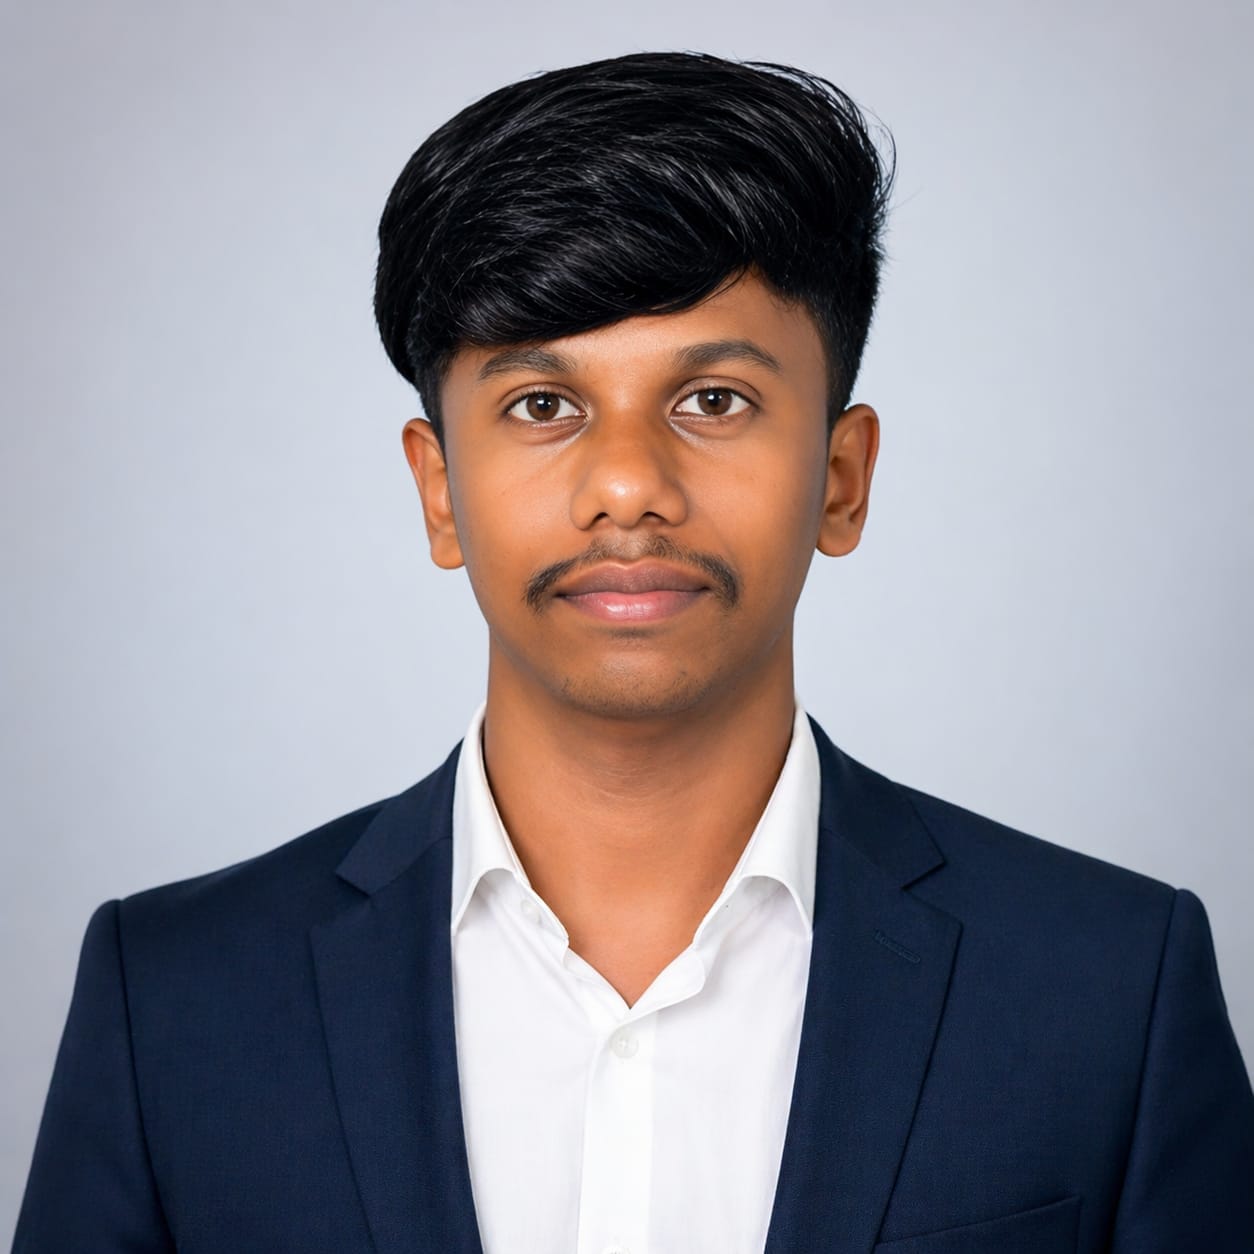
Hi 👋 I'm

Arava Anantha Rao

securing enterprises · empowering humans
Information Security Manager · GRC
🛡️
The MissionAspiring CISO — leading enterprise security from the front
💼 LinkedIn 9K+ followers
0+
Years @ TCS
0+
Client Accounts
0+
RFCs Reviewed
0K+
People Reached
0K+
Social Audience
Arava Anantha Rao
Available to Join Immediately
Open to InfoSec / GRC roles
Before you scroll

security starts with you.
whoever you are.

You don't need to be hacked to be exposed. Most breaches begin with everyday habits — let me show you one.

🔒
⚠ WEAK
Now, let me guess…
Felt familiar? Then you're already vulnerable. And a UPI ID like 9999999999@upi — built on your phone number — means you're leaving your personal information everywhere, with every payment. Breaches rarely start with code. They start with habits.

The strongest firewall in any organisation is an aware human being — an awareness I've delivered to 20,000+ professionals, one conversation at a time.

🕵️ SecAware Check

are you secaware
as an individual?

Ten quick questions. No sign-up. Discover your security-awareness score — then download a shareable certificate with your name on it.

⏱️ ~60 seconds🎓 instant certificate🔒 nothing stored
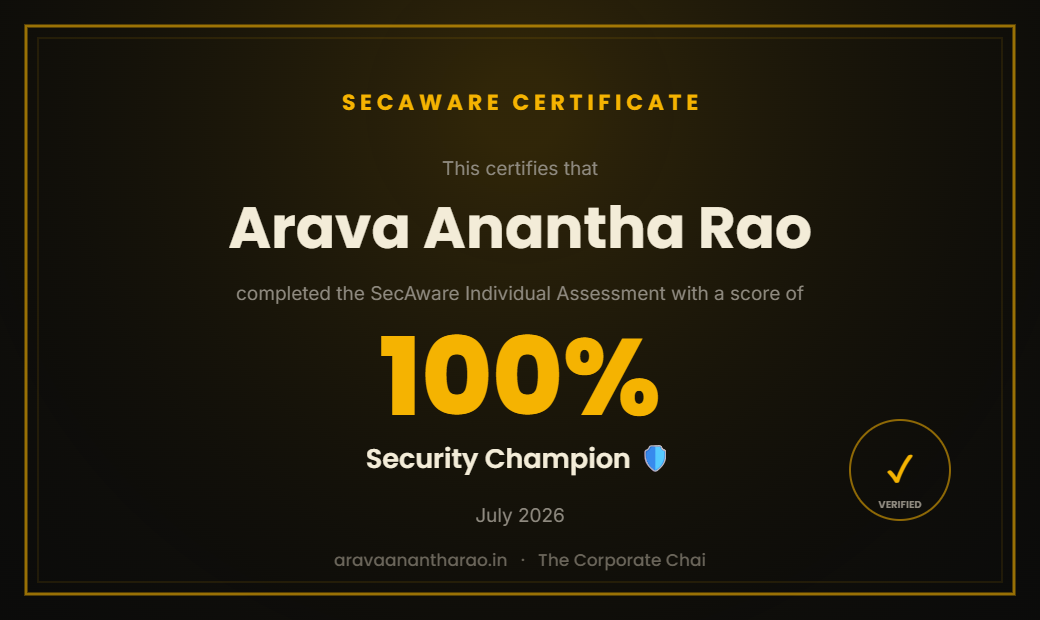
🎓 A peek at what you'll earn
Sample SecAware Certificate
My score? 100% — Security Champion 🛡️. Beat it.
🎮 Career Quest

every level, earned.

My journey — played like a game. XP gained, quests cleared, next boss level loading.

⭐ Player · A. Anantha Rao 🧭 Class · GRC Specialist ❤️ Streak · 3+ Yrs
01
Level 01 · Origin Story
Bachelor of Science
2018 — 2021
Maharaja's Autonomous College, Vizianagaram
CGPA 9.02
🏅 First Class with Distinction
02
Level 02 · Skill Tree Unlocked
Master of Computer Applications
2021 — 2023
Gayatri Vidya Parishad College of Engineering, Visakhapatnam
CGPA 8.84
🏅 First Class with Distinction
03
Level 03 · Main Quest — Completed
Information Security Manager · GRC
Sep 2023 — Oct 2026
Tata Consultancy Services (TCS), Hyderabad · Corporate Security
✓Owned the information security GRC program for a global business group — 75+ client accounts
✓Maintained the risk register — risk assessments, treatment plans & mitigation to closure
✓Translated client MSA obligations into Security Controls Identification (SCI)
✓Reviewed 500+ RFCs, change requests & POCs against ISO 27001 & NIST CSF
✓Monthly security scorecards & KPI/KRI decks for security committee meetings
✓Led audit readiness & SOC 2 evidence mapping — zero repeat findings
✓Access governance — compliance profiles, RBAC, least privilege, SoD
✓TPRM, vendor risk, RFP/RFI & GenAI risk assessments with Legal & Privacy
✓Incident analysis & RCA, firewall rule & VA exception reviews
✓Reassessed physical security across 6 Hyderabad campuses
✓Designed a cross-audit program, SOPs & baseline controls for HR, Admin & IT
✓Cut compliance reporting effort 30% with Copilot agents · L2 support & backup to team lead
🔒
Boss Level · Loading...
Chief Information Security Officer
The Goal
XP 38%

Grinding XP: leadership · strategy · certifications · scale. Every audit, every campaign, every risk call — one step closer.

🏆 Achievements Unlocked
🎖️Achievement Unlocked
Star Performer & Special Initiative
2024 & 2025 · back-to-back awards from the TCS CISO
🔍 View Certificates
⚡Achievement Unlocked
tcsAI ACCESS.AI SPARK
2026 · innovation at the TCS ACCESS.AI Hackathon
🔍 View Certificate
🛡️Achievement Unlocked
Zero Repeat Audit Findings
sustained across internal & external audit cycles for a 75+ account portfolio
🤖Achievement Unlocked
30% Less Manual Reporting
automated compliance reporting & leadership decks with Microsoft Copilot agents
Domains of practice

what i bring to the table

Nine domains of governance, risk & compliance I own end-to-end — straight from my day-to-day.

🏛️
DOMAIN 01

Governance & Compliance

ISO 27001:2022NIST CSFNIST RMFSOC 2CIS BenchmarksCISO / Leadership DecksSOP DesignSecurity Awareness
🎯
DOMAIN 02

Risk Management

Risk RegisterRisk AssessmentRisk TreatmentTPRMVendor RiskKRI & MetricsGenAI Risk
🔎
DOMAIN 03

Audit & Assurance

Audit ReadinessControl WalkthroughsEvidence ValidationGap AssessmentNC ClosureCross-Audit
⚖️
DOMAIN 04

Regulatory & Privacy

GDPRHIPAAPCI DSSDPDP ActData Protection
📋
DOMAIN 05

Client & Contractual Governance

MSA → SCISecurity ScorecardsRFC GovernanceRFP / RFICompliance Profiles
🔐
DOMAIN 06

ITGC & Access Management

Access ReviewsRBACLeast PrivilegeSegregation of Duties
🚨
DOMAIN 07

Security Operations

Incident MgmtRCAVA Exception ReviewsChange MgmtHardening (CIS)
🌐
DOMAIN 08

Information Security (Network, Cloud)

Network SecurityFirewall Rule ReviewsAzure SecurityAZ-500Shared ResponsibilityCloud Control Assessment
🏢
DOMAIN 09

Physical Security

Site Security Controls6-Campus ReassessmentPhysical Spot ChecksBuilding HOTO ReadinessAsset Security
Verified credentials

certified. proven.

Tap any credential to view the certificate.

2025

ISO/IEC 27001:2022 Lead Auditor

TÜV SÜD

2026

ISO/IEC 27701:2025 Lead Auditor

Mastermind · Certificate of Competency

2025

CompTIA Security+ (SY0-701)

CompTIA

2025

Azure Security Engineer Associate

Microsoft · AZ-500

2026

Microsoft Certified: AI Business Professional

Microsoft · Jul 2026

2024

Security, Compliance & Identity

Microsoft · SC-900

2024

Azure AI Fundamentals

Microsoft · AI-900

—

Azure Fundamentals

Microsoft · AZ-900

2026

DPDP Act 2023 — Certified · 93%

Digital Personal Data Protection

Get in touch

let's build something
secure together.

InfoSec & GRC opportunities, advisory conversations, speaking, mentoring — my inbox is always open. Chai's on me. ☕

aravaanantharao@gmail.com
🕵️ Quick challenge

Are you SecAware?

Honestly… I bet you'll fail. 10 questions, 60 seconds — prove me wrong and grab your certificate.

SecAware · Individual Assessment
Question 1 / 10
0%
Tip: your certificate downloads as an image — attach it to your LinkedIn post.